September 23, 2026
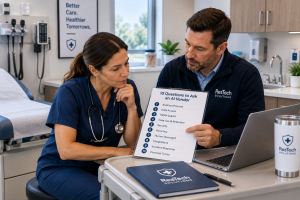 Before a healthcare practice buys an AI tool, it should ask the vendor 10 questions covering the business purpose, data access, HIPAA responsibilities, data use and retention, security, accuracy, human oversight, integrations, incident response, and contract terms.
The most important question is not simply, “What can the AI do?” It is, “What information will this tool access, what will it do with that information, and what risks will our practice still be responsible for?”
That distinction matters because AI tools now range from administrative assistants and documentation tools to patient-facing chatbots and clinical decision support. The risks change significantly depending on what the tool does and whether it creates, receives, maintains, or transmits protected health information (PHI). HHS specifically identifies third-party AI chatbots that handle PHI for services such as symptom assessment, reminders, or appointment scheduling as an example of a business associate.
For an independent healthcare practice, these 10 questions provide a practical vendor-evaluation framework before approving an AI purchase.
Why Does an AI Tool Need More Review Than a Typical Software Purchase?
AI can make an ordinary software decision more complicated because the system may not simply store or display information. Depending on the product, it may analyze information, generate new content, make recommendations, summarize conversations, interact with patients, or influence employee decisions.
A Practice Administrator evaluating an AI tool therefore needs to understand several different issues at once:
- What problem is the practice trying to solve?
- What information will the AI receive?
- Where does that information go?
- How can the vendor use it?
- How is the system secured?
- How reliable are its outputs?
- What happens when it makes a mistake?
- Who remains responsible for reviewing its work?
- What happens to the practice's information when the relationship ends?
HIPAA does not prohibit healthcare organizations from using cloud-based technology that handles ePHI. However, when a cloud service provider creates, receives, maintains, or transmits ePHI on behalf of a covered entity, HHS states that the provider is a business associate and a HIPAA-compliant Business Associate Agreement (BAA) is required. The healthcare organization must also understand the service well enough to conduct its own risk analysis and risk management.
The same principle is important when evaluating AI: a vendor saying its product is “HIPAA compliant” does not eliminate the practice's responsibility to understand how the tool will actually be used.
What 10 Questions Should You Ask an AI Vendor?
The questions below should be answered before the practice approves the tool, particularly when employees may use it with patient information or to support clinical or operational decisions.
1. What Specific Problem Is Your AI Tool Supposed to Solve?
Start with the business problem, not the technology.
Ask the vendor to explain:
- The tool's intended use
- Who is expected to use it
- Which workflows it supports
- What tasks it automates or assists
- What decisions it is intended to influence
- What measurable improvement customers should expect
A tool designed to draft marketing content creates a very different risk profile from an AI medical scribe, patient chatbot, coding assistant, or clinical decision support system.
The practice should also define its own expected outcome.
For example, if an AI documentation tool is being considered because physicians spend too much time completing notes, establish what success would look like before buying it. That might include less documentation time, fewer after-hours charting tasks, or faster completion of notes.
Otherwise, the practice may end up paying for AI without knowing whether it actually solved the original problem.
2. What Practice and Patient Data Will the AI Access?
Ask the vendor exactly what information the tool will create, receive, collect, process, or store.
Depending on the application, that could include:
- Patient names and demographic information
- Clinical notes
- Audio recordings
- Appointment information
- Billing information
- EHR data
- Documents
- Employee information
- Login or identity information
- Device or usage information
Don't stop at information employees intentionally enter into the AI.
Ask whether the product automatically collects information through integrations, browser extensions, meeting recordings, APIs, EHR connections, telemetry, logs, or other mechanisms.
Then determine whether any of that information could be PHI or other sensitive practice data.
This is also a useful point to involve the practice's IT provider. A new AI application may interact with Microsoft 365, employee accounts, devices, cloud applications, or other parts of the technology environment that the vendor evaluation team may not initially consider.
3. Will You Sign a Business Associate Agreement When Required?
If the vendor will create, receive, maintain, or transmit PHI on behalf of the practice in a way that makes it a business associate, ask whether the vendor will execute an appropriate BAA.
Do not treat a statement such as “HIPAA-ready,” “HIPAA-enabled,” or “HIPAA compliant” as a substitute for understanding the actual relationship.
HHS states that a business associate contract establishes permitted and required uses and disclosures of PHI and requires the business associate to implement appropriate safeguards. It also addresses reporting, subcontractors, termination, and other responsibilities.
Ask:
- Is a BAA available for this specific product?
- Is it included with our subscription level?
- Are there features that are excluded from the BAA?
- Does the BAA cover the way we intend to use the product?
- Which subcontractors or subprocessors may handle PHI?
The last question is particularly important. A vendor may rely on other companies to provide hosting, AI models, transcription, analytics, or other components.
HHS requires business associates to ensure applicable subcontractors that access PHI agree to appropriate restrictions and conditions.
4. How Do You Use, Retain, and Delete Our Data?
This question deserves a detailed answer.
Ask the vendor:
- How long is our information retained?
- Can we configure the retention period?
- Is deleted information removed from backups?
- Is our information used to train or improve AI models?
- Is it used to improve services for other customers?
- Can we opt out of secondary uses?
- Is information shared with other companies?
- What happens to our information when we cancel?
- Can we export our data before termination?
The practice should distinguish between using information to provide the contracted service and using that information for other purposes.
HHS explains that business associate agreements should define permitted uses and disclosures of PHI, and the parties can further restrict how that information may be used.
For AI tools, this question becomes especially important because “using your data” can mean more than simply storing it.
Get the answer in writing.
5. How Do You Protect Our Data and Accounts?
A BAA does not replace technical security.
Ask the AI vendor what controls protect the product and the practice's information.
Relevant questions may include:
- Does the platform support multifactor authentication?
- Can the practice use single sign-on?
- Can administrators control employee access?
- Are permissions role-based?
- Is data encrypted in transit and at rest?
- Can administrators review audit or activity logs?
- Can access be quickly removed when an employee leaves?
- How are vulnerabilities identified and remediated?
- How are customer environments separated?
- What security assessments or independent audits does the vendor undergo?
The practice should also determine how the AI tool fits into its existing employee access process.
A new AI platform means another set of accounts, permissions, and potentially sensitive information that must be managed throughout an employee's lifecycle.
For additional guidance, see How Should Healthcare Practices Manage IT Access When Employees Are Hired or Leave? A 7-Step Process.
6. How Accurate Is the AI, and How Do You Measure Its Performance?
Do not accept “our AI is highly accurate” without asking what that actually means.
Ask:
- What does the vendor mean by accuracy?
- How was the system tested?
- What population or data was used for validation?
- What are its known limitations?
- What types of errors occur most often?
- Does performance vary by specialty, patient population, workflow, or use case?
- How does the vendor monitor performance after deployment?
- How are customers informed when the model or product changes?
These questions become increasingly important when an AI system affects clinical decisions.
The FDA's current clinical decision support guidance emphasizes that healthcare professionals may need information about a product's intended use, required inputs, underlying methods, data relied upon, and validation so they can independently review the basis for a recommendation.
Likewise, federal transparency requirements for certain predictive decision support interventions in certified health IT are intended to provide clinical users with information that helps them assess fairness, appropriateness, validity, effectiveness, and safety.
Not every AI tool falls under those particular regulatory requirements, but the underlying purchasing lesson is useful:
The more an AI system can influence patient care, the more important it becomes to understand how its output was produced and validated.
7. Where Is Human Review Required?
Ask the vendor what it expects a person to verify before an AI-generated result is used.
This could involve:
- Reviewing an AI-generated clinical note before signing it
- Verifying coding recommendations
- Checking patient communications before sending them
- Reviewing summaries for missing information
- Confirming recommendations before acting on them
- Escalating uncertain outputs to a qualified person
Then define the practice's own rules.
An AI tool should not quietly change who is accountable for a task simply because the technology can perform part of it.
For higher-risk applications, ask the vendor what happens when the AI is uncertain, receives incomplete information, or produces an unexpected result.
NIST's AI Risk Management Framework is designed around managing AI risks to individuals and organizations, and its generative AI profile addresses risks specific to generative systems.
The practical takeaway for a small healthcare practice is straightforward: know where automation stops and human judgment begins.
8. What Systems Does the AI Integrate With, and What Permissions Does It Need?
Integration can be one of an AI product's biggest benefits, but it can also expand the amount of information and technology the vendor can access.
Ask whether the tool connects with:
- The EHR
- Practice-management software
- Microsoft 365 / Email
- Calendars
- Cloud storage
- Patient portals
- Billing systems
- Phones or call recordings
- Other clinical applications
For each integration, ask:
What permissions does the AI actually need?
A scheduling assistant may not need broad access to email and files. A documentation tool may not need unrestricted access to the entire patient record.
The principle should be to provide the access necessary for the approved purpose rather than granting broad permissions simply because the integration supports them.
The practice's IT provider should review significant integrations before implementation, particularly when the tool connects to Microsoft 365, identity systems, endpoints, networks, or other business-critical technology.
This follows the same principle discussed in How Should Healthcare Practices Manage IT Vendors Without Getting Caught in the Middle? A 7-Step Process: involve IT before a technology change rather than after something breaks.
9. What Happens If There Is a Security Incident or the AI Fails?
Ask the vendor to explain both its cybersecurity response and its operational response.
Questions should include:
- How will you notify us of a security incident?
- What information will you provide?
- What are your contractual notification requirements?
- Who is our escalation contact?
- What happens if the service becomes unavailable?
- Is there a documented disaster-recovery process?
- How is our data backed up?
- What service commitments apply?
- How can the practice continue operating without the AI?
- How are serious product errors reported and corrected?
This matters because the practice may eventually build workflows around the tool.
An AI scribe that starts as a convenience can become something physicians rely on every day. A scheduling assistant may become part of patient communications. An AI tool integrated with the EHR may become embedded in clinical workflows.
The more important the tool becomes, the more important its downtime and recovery procedures become.
Healthcare practices should incorporate critical vendors into their broader business continuity planning rather than assuming the vendor will always be available. Our 7-part healthcare business continuity checklist provides a framework for that planning.
10. What Are the Full Contract, Pricing, and Exit Terms?
Finally, understand the business relationship before signing.
Ask about:
- Subscription price
- Per-user or usage-based fees
- Implementation costs
- Training costs
- Integration fees
- Minimum commitments
- Automatic renewals
- Price increases
- Support costs
- Data-export fees
- Termination requirements
- Data-retention terms after cancellation
- Ownership of practice data
- Ownership of AI-generated output
- Product changes during the contract
- Vendor rights to change features or models
AI pricing can become difficult to predict when costs are based on usage, minutes, transactions, tokens, encounters, or other variables.
Model the expected cost using the practice's actual workflow.
For example, if an AI scribe is priced per provider or per encounter, estimate what the practice would spend using its actual number of clinicians and patient visits. Then compare that cost against the specific operational improvement the practice expects to achieve.
Also plan for the possibility that the relationship ends.
The practice should know how to retrieve its information, how long the vendor retains copies, what happens to integrations and accounts, and how operations would transition to another solution.
How Should a Healthcare Practice Evaluate the Vendor's Answers?
A vendor answering all 10 questions does not automatically make the product appropriate.
The answers still need to be evaluated against the practice's intended use.
A simple review can look like this:
| Area | What the Practice Should Confirm |
| Business purpose | The tool solves a defined problem with measurable goals |
| Data access | The practice knows what information the AI can access |
| HIPAA relationship | BAA requirements and responsibilities are understood |
| Data use | Retention, deletion, training, and secondary uses are documented |
| Security | Appropriate account, access, encryption, and monitoring controls exist |
| Accuracy | Performance claims, limitations, and validation are understood |
| Human oversight | Employees know what must be reviewed before use |
| Integrations | Permissions are limited to what the approved use requires |
| Incident response | Security, downtime, escalation, and recovery processes are defined |
| Contract and exit | Total cost, renewal, ownership, export, and termination terms are understood |
The practice should document this review rather than relying on a sales demonstration or email conversation.
It is also reasonable for different people to review different portions. A Practice Administrator may own the business case and workflow. The IT provider can evaluate integrations, accounts, security, and technical requirements. Privacy, compliance, clinical, or legal expertise may be needed depending on the tool and its intended use.
The higher the potential impact on patients, PHI, clinical decisions, or critical operations, the more scrutiny the product deserves.
Does FDA Authorization Matter for a Healthcare AI Tool?
Sometimes.
Not every healthcare AI product is a medical device, and not every software product marketed to healthcare organizations falls under FDA medical-device oversight.
However, if the vendor claims that its AI performs functions that may constitute a medical device, ask the vendor to explain the product's regulatory status and provide supporting information.
The FDA maintains an AI-Enabled Medical Device List identifying AI-enabled devices authorized for marketing in the United States. The agency notes that products on the list have met applicable premarket requirements, including review of safety and effectiveness for their intended use.
FDA also issued updated final guidance on Clinical Decision Support Software in January 2026. Some CDS software functions are excluded from the statutory definition of a medical device, while others remain subject to FDA oversight.
For an administrative AI tool that summarizes internal meetings, FDA status may be irrelevant.
For AI that analyzes medical information or influences clinical decision-making, the question can become much more important.
Don't assume that “AI for healthcare” means the product has been reviewed or authorized by FDA.
Frequently Asked Questions
Can a Healthcare Practice Put PHI Into an AI Tool?
Potentially, but the answer depends on the tool, the intended use, how the vendor handles the information, the contractual relationship, and whether the practice's HIPAA obligations are satisfied.
When a vendor creates, receives, maintains, or transmits PHI on behalf of a covered entity as a business associate, HIPAA generally requires an appropriate BAA and safeguards.
Employees should not independently decide that a public or newly discovered AI tool is appropriate for PHI simply because the product is available.
Does a BAA Mean an AI Tool Is Safe to Use?
No.
A BAA addresses important HIPAA responsibilities and permitted uses and disclosures, but the practice still needs to evaluate security, access, data handling, the intended use, integrations, reliability, human oversight, and operational risk.
A signed BAA is one part of the evaluation, not the entire evaluation.
Should Employees Be Allowed to Choose Their Own AI Tools?
A healthcare practice should establish an approval process for AI tools that may interact with practice information, accounts, workflows, or patient data.
Without one, employees may adopt tools before anyone has evaluated data handling, contractual terms, security, integrations, or whether the product is appropriate for the intended use.
Should the Practice's IT Provider Review an AI Tool Before Purchase?
For AI tools that connect to the practice's technology, access business or patient information, create employee accounts, or integrate with systems such as Microsoft 365 or the EHR, involving the IT provider before purchase can identify technical and security issues before the product is deployed.
That does not mean IT should make the entire purchasing decision. The business owner, Practice Administrator, clinical leadership, compliance resources, and other appropriate stakeholders may all have responsibilities depending on the product.
How Often Should an Approved AI Tool Be Reviewed?
Approval should not be treated as permanent.
Review the tool when the vendor materially changes its product, AI model, integrations, data practices, subprocessors, security terms, or contract. The practice should also reassess the tool when its own use changes.
A product originally approved for a low-risk administrative task may require a different review if employees later begin using it with PHI or for clinical workflows.
Final Thoughts
Healthcare practices should evaluate AI vendors based on more than features and demonstrations.
Before approving an AI tool, understand why the practice needs it, what information it can access, how the vendor uses and protects that information, how reliable its outputs are, where human review is required, what systems it connects to, and what happens when something goes wrong or the relationship ends.
Those 10 questions create a repeatable purchasing process rather than forcing the Practice Administrator to evaluate every new AI product from scratch.
AI can create meaningful value for a healthcare practice. The objective is to adopt it intentionally, with enough information to understand both the opportunity and the responsibility that comes with it.
About ResTech Solutions
ResTech Solutions helps independent healthcare practices throughout the Houston area manage and secure the technology their teams rely on, including Microsoft 365, cybersecurity, user access, cloud applications, vendor relationships, and ongoing technology planning.
When a practice considers a new AI platform, the technology decision does not happen in isolation. The tool may introduce new accounts, integrations, permissions, data flows, vendor dependencies, and cybersecurity considerations that should be understood before implementation.
If your practice is evaluating an AI tool and wants help reviewing how it fits into your existing technology and security environment, book a 10-minute discovery call and we'll help you identify the technology questions that deserve attention before you move forward.